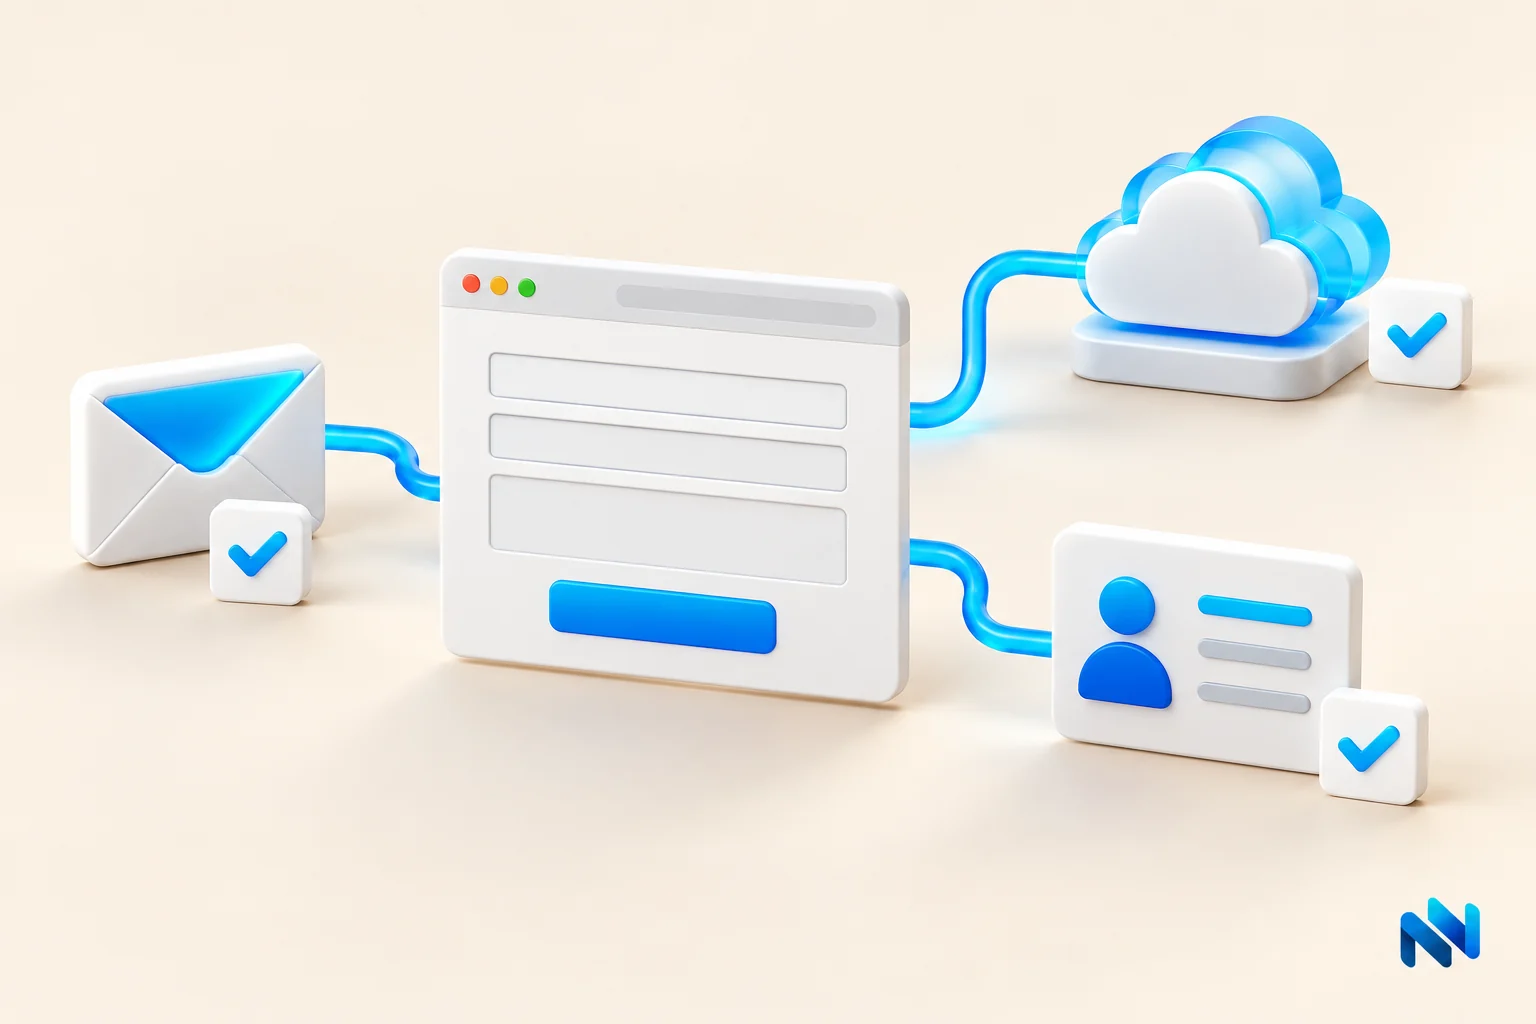
A visitor fills your enquiry form. Your website sends the details to an inbox, saves a copy in WordPress and passes another copy to a CRM. Meanwhile, an advertising pixel records the visit.
Do you know where each copy goes, why it is needed and when it will be deleted? That is a useful starting point for this DPDP website checklist for 2026.
India’s Digital Personal Data Protection framework asks businesses to take responsibility for the personal data they handle. For a website owner, the work involves forms, tracking tools, access controls and everyday office processes. A banner alone will not cover all of it.
When do India’s DPDP rules take effect?
The final DPDP Rules notification is dated 13 November 2025 and sets out a phased commencement. Some provisions started immediately, while the main operational rules have an 18-month transition.
For planning, work towards 13 May 2027. A May 2026 government statement identifies that date for full enforceability. You may also see 14 May 2027 in commentary based on the publication date. Do not leave your implementation dependent on that one-day difference. Confirm the applicable notifications before your final legal review.
In October 2026, this is preparation for the main obligations. It does not mean every DPDP requirement or penalty is already operational, or that existing privacy and security duties can be ignored.
A practical DPDP website checklist for 2026
1. List every place your website collects information
Open your website as a new visitor and work through every journey. Include contact forms, job applications, checkout, newsletter sign-ups, live chat and appointment bookings.
Make a simple sheet with five columns: information collected, purpose, destination, people with access and retention period. Include details collected behind the scenes, such as visitor identifiers and server logs, where they can relate to an identifiable person.
Check the inbox as well as the website database. A form plugin may delete an entry while a downloaded spreadsheet or forwarded email remains with a team member.
2. Decide why each field is needed
A request for a callback may need a phone number. It usually does not need a date of birth or home address. Look at each mandatory field and ask your team what they actually do with it.
Under sections 4 and 7 of the DPDP Act, 2023, consent and specified legitimate uses are distinct grounds for processing. Do not assume every activity needs the same checkbox, or that submitting an enquiry permits unrelated marketing.
Record the basis for each use with your legal adviser. Then ask your developer to remove unnecessary fields and stop sending unused information to other tools.
3. Put a clear notice beside the form
Rule 3 requires an understandable notice explaining the personal data and its purposes, along with ways to withdraw consent, exercise rights and complain. Give visitors useful information before they make a choice.
For example, a callback form could explain that your team will use the submitted name and number to respond to that request. Link to the detailed privacy notice nearby. Avoid a long, vague statement about using information to improve services.
Read the notice on a phone. If the link is hard to tap, the text is tiny or the explanation is hidden below the submit button, improve the layout.
4. Remove pre-ticked consent boxes
Section 6 requires a clear affirmative action for consent. Use an unticked choice where you rely on consent. Silence, scrolling and a box selected by default should not be treated as a visitor’s agreement.
Keep optional promotional messages separate from the enquiry itself. Someone asking for a quotation should be able to understand whether they are also signing up for offers.
Test what happens when the optional box is left empty. Your website should not quietly add that person to a marketing list.
5. Check what loads before a visitor agrees
A consent banner can look correct while scripts continue running underneath it. Ask your developer to inspect network requests, cookies and browser storage on a fresh visit.
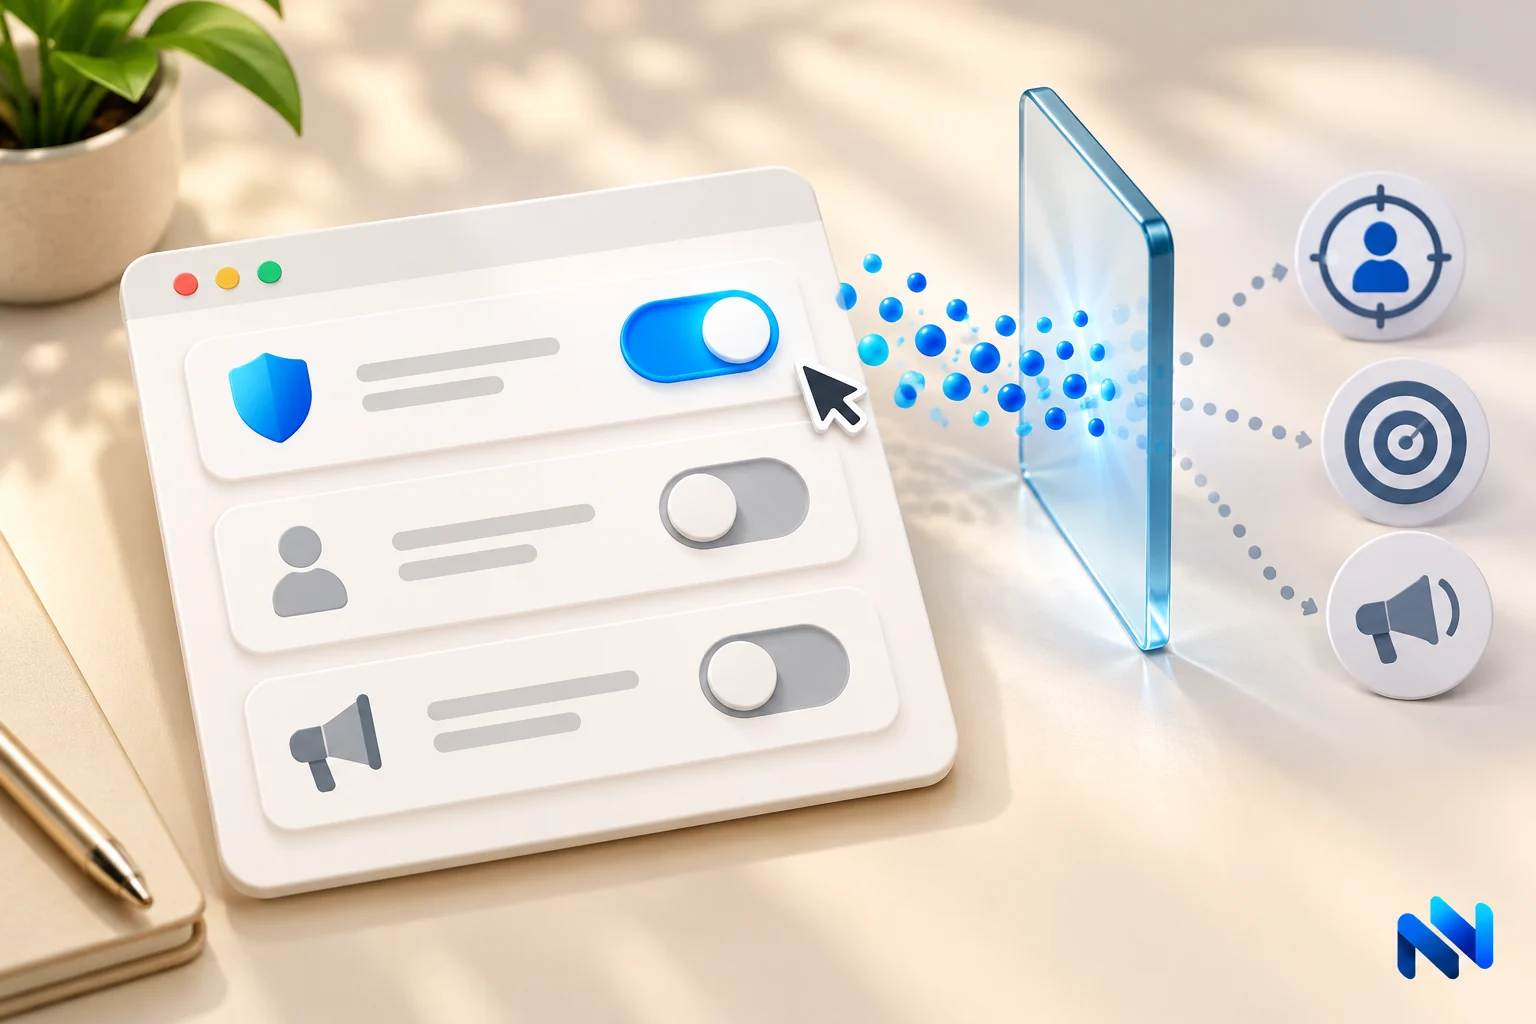
Where analytics or advertising tools process personal data on a consent basis, keep that processing off until the visitor opts in. Review embedded videos, chat widgets and tag-manager rules too. A setting inside one plugin may not control a script added elsewhere.
DPDP is not a blanket rule that every cookie needs consent. Assess the personal data, purpose and applicable basis. Necessary website functions and optional advertising should not simply be put into one category.
6. Make changing a choice straightforward
Add a clearly named privacy preferences link where visitors can find it again. Test accepting, rejecting, selecting individual purposes and withdrawing later.
After withdrawal, revisit another page and reload the site. Check that the earlier choice has not been restored by a second plugin. Keep an appropriate record of the choice and notice version without collecting extra identifiers just for convenience.
7. Agree retention periods across the business
Decide how long enquiries, applications and other records are needed. Document the reason, any legal retention requirement and the person responsible for deletion.
There is no universal 30-day retention period for every Indian business. A period suitable for an unanswered enquiry may not suit an invoice or an active service contract.
Cover WordPress entries, inboxes, CRM records, exports and backup handling. If deletion is manual, describe it honestly. Do not promise automatic removal in your privacy policy until that process exists and has been tested.
8. Review access, hosting and service providers
List everyone who can view or export submissions. Remove unused staff accounts, avoid shared administrator logins and give each person only the access their work needs.
Check updates, secure connections, private file storage and recovery procedures. Review what your hosting, form, email and CRM providers do with the information they receive. Ask for clear contractual responsibilities rather than relying on a plugin’s marketing label.
If your setup has grown through years of small additions, a website development review can help identify duplicate forms, forgotten scripts and unnecessary integrations.
9. Give privacy requests and incidents an owner
Choose a monitored contact route for privacy requests. Prepare a short internal process covering who checks a request, who searches the systems and who records the response.
Prepare for a data incident too. Keep the hosting contact, developer contact and internal decision-maker in one place. Practise with a fictional example, such as an application attachment becoming publicly accessible.
The Rules contain breach notification requirements, including an initial Board notification without delay and further details within 72 hours unless more time is allowed. Your incident plan should cover the Board and affected individuals, with legal guidance on the applicable requirements.
10. Keep evidence of the checks
Maintain a dated folder containing your data inventory, notice versions, consent tests, access review and deletion procedure. Save screenshots and technical observations without exposing real customer details.
Repeat the checks after adding a form, chat tool, campaign pixel or new CRM connection. A website can pass today’s review and change next week when someone installs a plugin.
Can the penalty really reach Rs. 250 crore?
Yes. The government’s DPDP explainer states that failure to maintain reasonable security safeguards can attract a penalty up to Rs. 250 crore. Other breaches have different maximum amounts.
That is not an automatic fine for a missing banner. It is a reason to take the wider handling of personal data seriously, including the systems behind the website.
Common questions from website owners
Does a small business need to prepare?
Yes, if its activities fall within the framework. Do not assume a low visitor count or small team creates a general exemption. Review your actual processing and any applicable notified exemptions.
Will installing a consent plugin make the site compliant?
A plugin can help manage choices. You still need to check its configuration, connected scripts, notices, records and the way your team handles submissions.
Should we remove analytics completely?
Review what your analytics collects and why. You may be able to reduce collection or use a suitable consent-based setup. Ask for a technical assessment before making changes that affect reporting.
Start with your forms and tracking tools
Pick one customer journey this week. Submit a test enquiry, follow every copy and check which tools receive information before a visitor makes a choice. Give each issue an owner and a target date.
If you need help reviewing forms, implementing consent controls or cleaning up website integrations, talk to Netens about a technical website audit. Bring your developer and legal adviser into the review so the website behaviour and your documented policy agree.
Prepared on 21 October 2026. This is a technical preparation checklist, not a legal opinion or compliance certification. Check the latest notifications and obtain advice for your business before relying on a final implementation.